ISEC7 SOVEREIGN SUITE
Your mobile workplace stays in German hands
The ISEC7 SOVEREIGN SUITE bundles five building blocks for the mobile workplace: mail, data classification, device management, compliance monitoring and tap-proof telephony. Each building block runs on its own. The contractual partner and operator is the ISEC7 Group, headquartered in Hamburg, with German jurisdiction.
You don't have to replace your entire environment to get there. The usual starting point is ISEC7 MAIL or the Sovereign Cloud for BlackBerry UEM.
Book an initial consultation Take the sovereignty check first
No obligation. You can also reach us directly at sales@isec7.com or +49 40 325076 0.
Evidence at a glance
Contractual partner and jurisdiction
ISEC7 GmbH, HamburgOperational responsibility with the ISEC7 Group, German jurisdiction
UEM platform
BSI-DSZ-CC-1235-2025Common Criteria EAL 4+, issued on September 8, 2025, valid until September 7, 2030. Certificate holder: BlackBerry Limited
Voice communication
BSI deployment authorization up to VS-NfDBSI-VSA-11057 for SecuVOICE 6.x, valid until August 31, 2027. Holder: Secusmart GmbH, operated by ISEC7
Data center
ISO 27001 · BSI C5 · TSI Level 4Plus ISO 9001, BSI IT-Grundschutz and evidence under the German BSI Act (BSIG)
The Sovereign Cloud for BlackBerry UEM runs exclusively in German data centers. Responsibility for operations lies with the ISEC7 Group, not with the manufacturer of the platform.
The framework
How to recognize a sovereign cloud
By three things: the data is processed in Germany. Operational responsibility lies with a company headquartered in Germany. And in the event of a dispute, a German court decides.
The storage location alone covers only one of these points. That is down to the wording of the US CLOUD Act of 2018: under 18 U.S. Code § 2713, a provider must disclose data that is in its possession, custody or control, “regardless of whether such communication, record, or other information is located within or outside of the United States”. This requires a valid US legal order, and for content data a search warrant. So it is not blanket access. But anyone who bears responsibility as a public authority or KRITIS operator cannot avoid the question of who the operator is.
The European data protection authorities take a similar view. On June 5, 2025, the European Data Protection Board published the final version of its Guidelines 02/2024 on Article 48 GDPR: decisions by third-country authorities are not automatically enforceable in the EU, and the case of a parent company requesting data from its European subsidiary is explicitly addressed.
Regulation is heading the same way. On June 3, 2026, the European Commission proposed the Cloud and AI Development Act (COM(2026) 502, procedure 2026/0138 COD). It provides for a sovereignty framework with four Union Assurance Levels. So far this is a proposal at the preparatory stage in the European Parliament, not applicable law. Tenders, however, are already asking for the evidence today.
Independent sources
What public authorities and market research find
Three findings support the focus of this page, all from sources that do not come from ISEC7.
Public administration was the main target of cyber espionage
By far the largest number of the APT groups relevant to Germany targeted this sector, followed by foreign affairs, defense, the judiciary, and public safety and order.
BSI, The State of IT Security in Germany 2025, reporting period July 2024 to June 2025. bsi.bund.de/lageberichtAn average of 119 new vulnerabilities per day, an increase of around 24 percent
The BSI points out that part of the increase is due to a changed reporting policy. For operations, the consequence remains the same: anyone who has to prove patch levels across several platforms needs one view instead of four consoles.
BSI, The State of IT Security in Germany 2025, attack surface dimension. bsi.bund.de/lageberichtThe BSI itself is working on VS-NfD in the cloud
The BSI cloud strategy names as one goal processing classified information up to the VS-NfD level in clouds, and as a further goal making sovereign usage scenarios for European and national clouds competitive. A sovereign cloud for classified data is therefore an officially pursued field of work.
BSI, The State of IT Security in Germany 2024, cloud strategy, goals 2 and 3. bsi.bund.de/lageberichtOn certificates: as of June 30, 2025, the BSI held a total of 413 Common Criteria certificates, 105 of them newly issued during the reporting period. Certification is therefore an ongoing process, not a one-off act. Source: BSI situation report 2025.
Context
Four levels at which sovereignty can be measured
These four levels are our assessment grid, not a legal text. They hold up in a tender because each level depends on evidence, not on a promise.
Level 1
Data processing in the EU
Processing and storage take place within the EU. The entry level that most offerings work with today.
Level 2
Independence from third countries
The real test. What is required is evidence that no third-country law reaches into operations, not a contractual assurance.
Level 3
Ownership and personnel
Requirements for the ownership structure and for the personnel deployed. In the Regulated Sovereign Cloud, only personnel of ISEC7 GmbH in Germany carry out administration.
Level 4
Transparent supply chain
Complete control and traceability across the entire supply chain, including subcontractors.
What exists officially alongside it
Since October 2025, there has been an official grid: the Cloud Sovereignty Framework of the European Commission (version 1.2.1) assesses eight sovereignty objectives on the levels SEAL 0 to SEAL 4, from “No Sovereignty” to “Full Digital Sovereignty”. On April 27, 2026, the BSI followed with the Criteria enabling Cloud Computing Autonomy (C3A, version 1.0), there without levels.
Our four levels replace neither. They are the short version for an initial consultation, before anyone opens a 60-page criteria catalog.
To the sovereignty check Or book an initial consultation right away
Sovereignty check
How sovereign is your mobile workplace today?
Six questions along the four levels above, plus one on evidence. The check runs here on the page, in your browser. Nothing is stored and nothing is transmitted unless you transfer the result to your request yourself.
The questions cover the processing location, the operator of your UEM platform, evidence against third-country law, the requirements for the personnel administering your environment, the supply chain, and how you currently produce evidence of patch levels and certificate lifetimes. It takes about two minutes.
- Your result as a score from 0 to 100 across all five areas
- An assessment per area, from evidenced to open
- The result as text that you can transfer to your request
Your result
The score is a self-assessment, not an audit. It works as a basis for discussion: take it into your request, and we will talk about the areas that are still open for you.
Result text to copy
If you need more detail: the official grid is the European Commission Cloud Sovereignty Framework with the levels SEAL 0 to 4, supplemented by the BSI C3A criteria of April 27, 2026. Both are linked above.
The suite
Five building blocks, one operating model
Each building block runs on its own and can be introduced individually. Together they make up a mobile workplace whose operation, from email to phone call, stays in German hands.
ISEC7 MAIL
Secure mobile mail and PIM client for Exchange and Microsoft 365, developed in Hamburg and independent of the UEM manufacturer.
- S/MIME across multiple mailboxes
- Delegate rules, functional and group mailboxes, public folders
- Connects directly to your backend, with no provider cloud in between
- Rollout in around 30 minutes via Auto-Discover
ISEC7 CLASSIFY
Labeling and classification of sensitive data in Microsoft 365, Outlook, SharePoint and directly in ISEC7 MAIL.
- Several schemes in parallel: corporate, German federal government, NATO
- Automatic recipient check, unauthorized domains are blocked
- DoD 5200 compliant
- No-code console for administrators
Sovereign Cloud for BlackBerry UEM
UEM operations exclusively in German data centers, under the responsibility of the ISEC7 Group.
- Enterprise variant for companies and the public sector
- Regulated variant (indigo / KNOX Native) for public authorities and defense
- Exclusively German jurisdiction
- Neither the manufacturer nor third parties get access
ISEC7 SPHERE
Monitoring and compliance platform. It provides the auditable proof of the state that the other building blocks establish.
- Largest documented installation: 220,000 devices
- Compliance monitoring for CVEs, certificates and vulnerabilities
- INDIGO Compliance Monitoring for VS-NfD environments
- In use for more than 20 years
ISEC7 MANAGED SECURE VOICE
Managed service for secured telephony and short messages on the work device, based on SecuVOICE by Secusmart. Your employees dial as usual.
- BSI deployment authorization up to VS-NfD, BSI-VSA-11057, valid until August 31, 2027
- SNS standard, key material is requested from the BSI
- Cloud service in Germany according to BSI C5
- Operation and user support by ISEC7, not by your IT
Managed services from Hamburg
The bracket around all building blocks: consulting, migration and 24x7 operations by the ISEC7 Group, in the market since 2003.
- Cross-UEM migration during ongoing operations
- 24x7 support
- Consulting on NIS2, KRITIS and VS-NfD
- CyberRisk Check according to DIN SPEC 27076, a procedure initiated by the BSI
European alternatives
Each building block replaces a US product on its own
Anyone looking for European alternatives today is usually looking for a single category. The suite covers five of them, each with its own origin and its own operating model.
That is also why the building blocks can be introduced individually. You don't have to replace the entire chain to become independent at one point.
| Category | European alternative | Origin and operation |
|---|---|---|
| Mobile mail and PIM client | ISEC7 MAIL | Developed by the ISEC7 Group in Hamburg. Connects directly to your backend, with no provider cloud in between |
| Data classification and labeling | ISEC7 CLASSIFY | In-house development of the ISEC7 Group. Supports German federal and NATO schemes in parallel to the corporate scheme, DoD 5200 compliant |
| UEM operations from the cloud | Sovereign Cloud for BlackBerry UEM | Platform from BlackBerry, a Canadian company. Operated exclusively in German data centers by the ISEC7 Group |
| Endpoint monitoring and compliance evidence | ISEC7 SPHERE | In-house development of the ISEC7 Group, in use for more than 20 years. INDIGO Compliance Monitoring for VS-NfD environments |
| Tap-proof telephony and short messages | ISEC7 MANAGED SECURE VOICE | Managed service based on SecuVOICE by Secusmart. SNS standard, cloud service in Germany according to BSI C5, BSI deployment authorization up to VS-NfD (BSI-VSA-11057) |
The category column deliberately names the product type, not manufacturer names. Which products would actually be replaced in your case is something we clarify in the initial consultation.
In focus
Make calls as securely as German federal authorities
ISEC7 MANAGED SECURE VOICE works according to SNS, the standard for secure cross-network voice communication (Sichere Netzübergreifende Sprachkommunikation). The SecuVOICE solution used for iOS and Android holds a BSI deployment authorization up to the VS-NfD level, listed under BSI-VSA-11057 and valid until August 31, 2027.
VS-NfD stands for Verschlusssache, nur für den Dienstgebrauch (classified, for official use only). It is the lowest of the four classification levels under Section 4 (2) of the German Security Clearance Check Act, and it is set by the issuing agency, not by the manufacturer.
On the division of roles: the holder of the deployment authorization is Secusmart GmbH. The ISEC7 Group operates the service and is your contractual partner for it. Your employees dial as usual; operations and user support are handled by us.
When VS-NfD is a requirement
Here the deployment authorization decides, not the data sheet. The service comes with exactly the evidence that is requested in tenders and security concepts.
- BSI deployment authorization up to VS-NfD, BSI-VSA-11057
- SNS standard, key material is requested from the BSI
- Cloud service in Germany according to BSI C5
- For Apple and Samsung devices, iOS and Android
When VS-NfD is not a requirement
Even without a classification level, there are conversations whose content becomes expensive once it gets out. The level of protection is the same, only the occasion is different.
- Negotiations, acquisitions and investment talks
- Management and supervisory board calls
- Development projects and design data
- HR matters and internal investigations
- Calls from the home office and on business trips
Your IT stays out of it
The effort for your organization is limited to two workshops and support during rollout. We take care of the rest.
- Workshop I: briefing and functional overview
- Application for and secure delivery of the key material
- Workshop II: setup and configuration
- Rollout of the app via your MDM or UEM
- Functional tests, commissioning, ongoing operations and user support
Book an initial consultation To the ISEC7 MANAGED SECURE VOICE product page
Comparison
What each of the three operating models delivers
The two sovereign variants differ from the standard cloud mainly in who is responsible for operations and which law applies. The criteria are the same ones that tenders ask about.
| Criterion | Standard Cloud | Enterprise Sovereign Cloud | Regulated Sovereign Cloud |
|---|---|---|---|
| Data storage | Several countries | Germany only | Germany only |
| Operational responsibility | Manufacturer / hyperscaler | ISEC7 | ISEC7 |
| Manufacturer access | Possible | No | No |
| GDPR compliance | Limited | Yes | Yes |
| BSI conformity (indigo & KNOX Native) | No | No | Yes |
| German jurisdiction | No | Yes | Yes |
| Suitable for the public sector | Limited | Yes | Yes |
Infrastructure evidence: ISO 27001, ISO 9001, an attestation according to the BSI C5 criteria catalog, BSI IT-Grundschutz, TSI Level 4 for physical data center security, and evidence under the BSI Act for KRITIS operators.
Technology base
The platform underneath: BlackBerry UEM
As of September 2026, BlackBerry UEM is the only UEM solution with a BSI certification according to Common Criteria. Certificate BSI-DSZ-CC-1235-2025 was issued on September 8, 2025 and is valid until September 7, 2030; the certificate holder is BlackBerry Limited. That is why we recommend the platform for sovereignty projects: the evidence already exists and does not have to be produced first.
BlackBerry is a Canadian company and is therefore not subject to the US CLOUD Act. For day-to-day operations, there is also the fact that the platform is used in government environments worldwide and has been tested accordingly.
- BSI-certified according to Common Criteria, EAL 4 augmented by ALC_FLR.3, evaluated against protection profile BSI-CC-PP-0115-2021 for mobile device management
- FIPS 140-2, FIPS 140-3 in progress
- Single-port access with integrated VPN, including when connecting local resources
- One platform for cloud, on-premises, hybrid and Sovereign Cloud
- True multi-tenancy and true BYOD
- Around 25 years of experience in mobile device management
- Roadmap for post-quantum cryptography
“Your data, your rules.” Guiding theme of the ISEC7 webcast on the Sovereign Cloud for BlackBerry UEM, April 14, 2026
Certification is not approval
Two different instruments that are often mixed up in tenders. Common Criteria certification attests to the tested security properties of the platform. An approval or deployment authorization under the German classified information directive (VSA) permits the processing of classified information. Today, no UEM product is on the BSI list of approved IT security products; that list includes mobile platform solutions such as Apple indigo and Samsung Knox Native Solution.
And the certification belongs to the platform: the holder is BlackBerry as the manufacturer, while the ISEC7 Group is the operator and your contractual partner for operations. In an audit, the two are assessed separately.
What comes after
What still needs to be done after approval
Four things: introduce, operate, prove, be reachable. The ISEC7 Group takes care of these four.
Approvals, certifications and deployment authorizations sit with the products used, with the BSI and with the manufacturers. But a tested product on its own does not yet make a running environment, and it does not yet make an audit report either.
Rollout
Introduction during ongoing operations
Migration between UEM platforms without bringing service operations to a halt. Even at public authorities that serve the public in person.
Operations
24x7 from Hamburg
Responsibility for availability, patch level and configuration. Your IT keeps control and still does not have to provide the on-call service itself.
Evidence
What is presented in the audit
ISEC7 SPHERE continuously documents status, patch levels and certificate lifetimes. The audit report is therefore based on documented data.
Incident
Reachable, with names
A German contractual partner with named contacts. Escalation runs through named people.
Four services under one roof: vendor-neutral UEM operations, our own mail product, tap-proof telephony as a managed service, and Device as a Service. This combination is why tenders with mixed requirements end up with us.
Target groups
Who requests the suite today
Organizations where an approval or an audit report stands at the end of the procurement process.
Public authorities and public administration
VS-NfD environments, indigo projects, BOS. What counts here is evidence that already exists.
KRITIS operators
Energy, water, health, transport. NIS2, the EU directive on the cybersecurity of critical entities, requires verifiable measures that extend into the supply chain.
Defense and armaments
Sensitive workloads, a German contractual partner and German jurisdiction as a firm requirement.
Regulated companies
Finance, legal, automotive and industry with intellectual property worth protecting and DORA obligations.
Frequently asked questions
What we are asked most often
Four questions that almost always come up in the initial consultation. If yours is not among them, ask us in the form below.
Do I have to book the complete suite?
No. Each building block works on its own; the suite describes the full setup. The usual starting point is ISEC7 MAIL or the Sovereign Cloud for BlackBerry UEM.
Is BlackBerry UEM approved for VS-NfD?
No, and no other UEM product is either. BlackBerry UEM is BSI-certified according to Common Criteria (BSI-DSZ-CC-1235-2025, EAL 4 augmented by ALC_FLR.3). An approval or deployment authorization under the German classified information directive is held by the mobile platform solutions, such as Apple indigo and Samsung Knox Native Solution, and by individual applications such as SecuVOICE. Certification and approval are two different instruments of the BSI.
What evidence is available for the infrastructure?
ISO 27001, ISO 9001, an attestation according to the BSI C5 criteria catalog, BSI IT-Grundschutz, TSI Level 4 for physical data center security, and evidence under the BSI Act for KRITIS operators.
Is VS-NfD telephony worthwhile even without a classification requirement?
The level of protection can be used regardless of the occasion. Typical use cases outside the public sector are negotiations and acquisition talks, calls by management and the supervisory board, development projects and design data, HR matters, and calls from the home office and on business trips.
Next step
Book a no-obligation initial consultation
We go through your existing environment along the four levels and tell you which building blocks make a measurable difference for you.
And which do not. If it turns out that two of the five building blocks are not an option for you, that is a useful result.
Have you taken the sovereignty check? Then enter your result in the Message field below, or have it filled in automatically using the button in the check.
Prefer to contact us directly: sales@isec7.com, +49 40 325076 0.
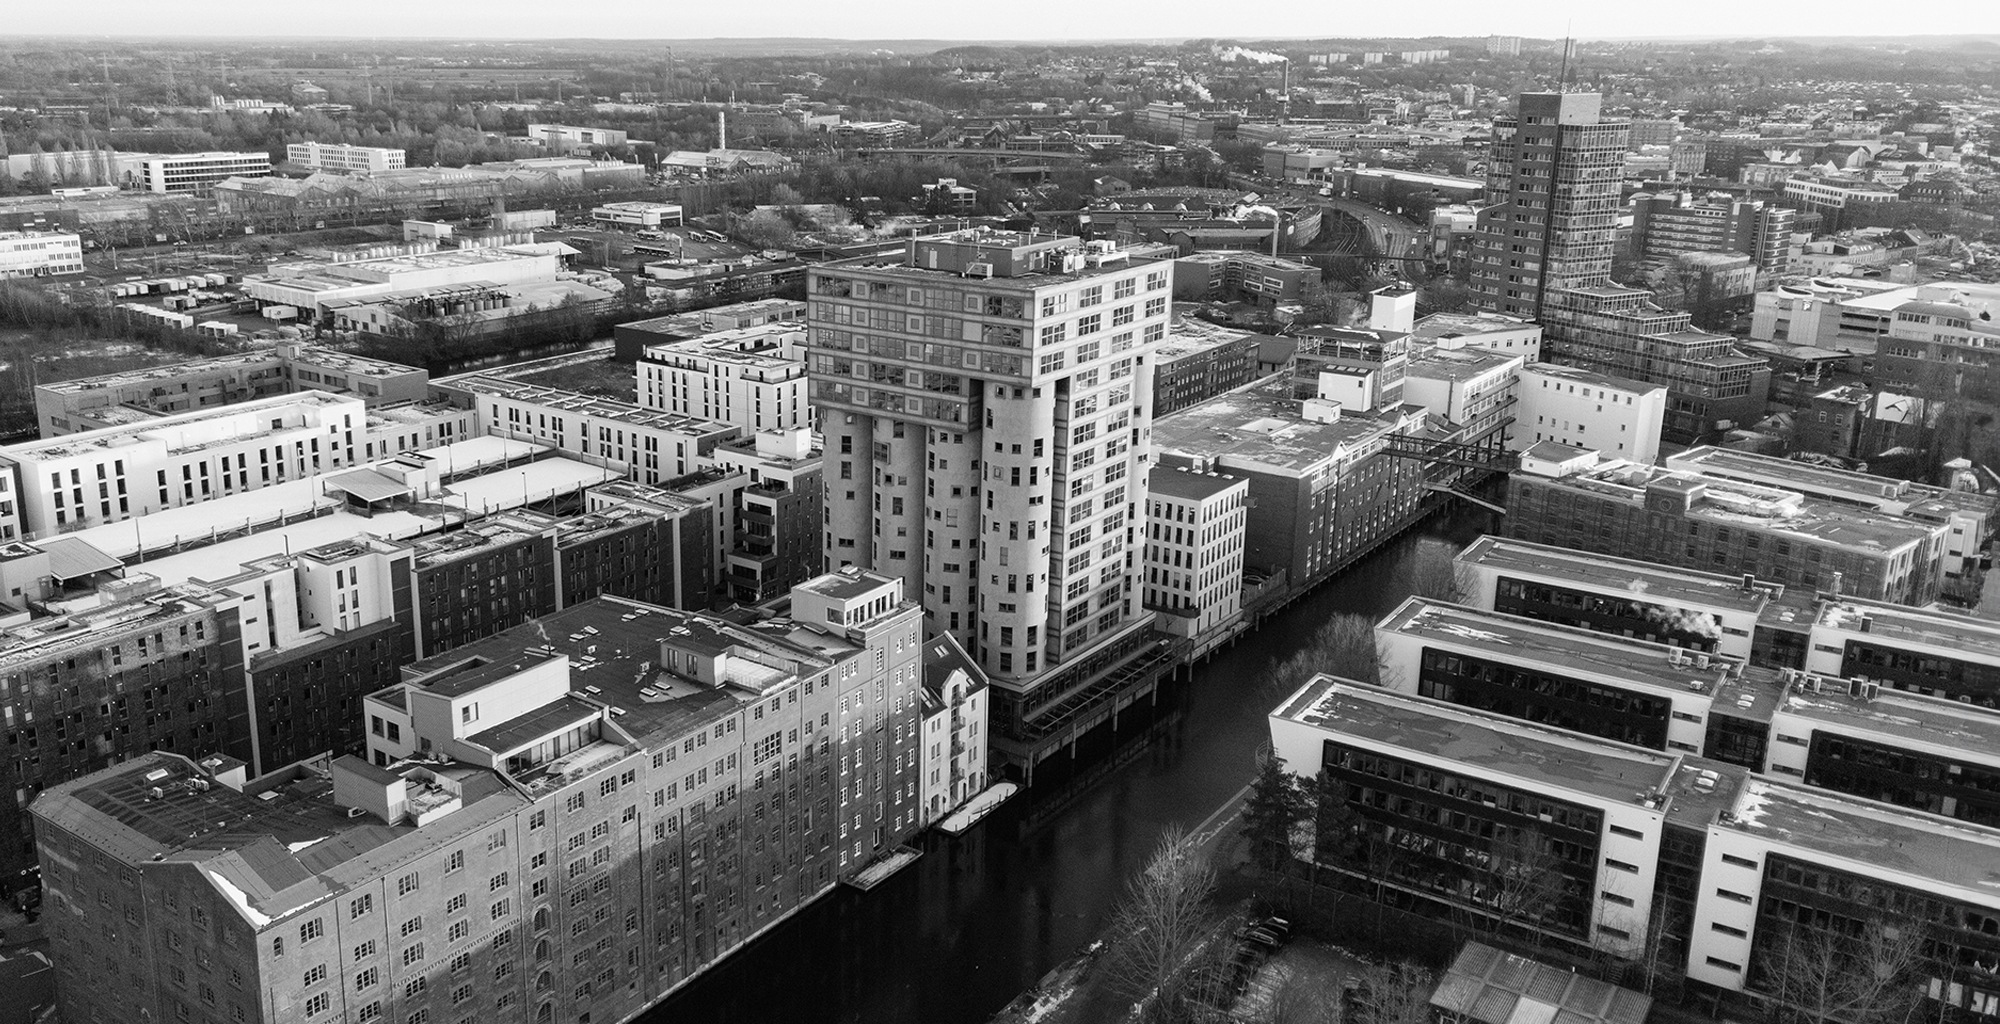
Hamburg-Harburg. This is where the ISEC7 Group is based, and this is where operations are run from.
Sources
What the information on this page is based on
- BSI, certification according to Common Criteriaofficial
Certificate BSI-DSZ-CC-1235-2025 for the BlackBerry Unified Endpoint Management Server, issued on September 8, 2025, valid until September 7, 2030. Certificate holder: BlackBerry Limited. EAL 4 augmented by ALC_FLR.3. bsi.bund.de, certificate 1235 - BSI, list of approved IT security products and systems (BSI publication 7164)official
SecuVOICE for iOS and Android, version 6.x, deployment authorization BSI-VSA-11057, up to VS-NfD, dated August 14, 2026, valid until August 31, 2027. Holder: Secusmart GmbH. List of approved products - BSI, VS product catalogofficial
Version 1.11.1 of January 23, 2026. Source for the distinction between approval, deployment authorization and release. VS product catalog (PDF) - European Commission, Cloud Sovereignty Frameworkofficial
Version 1.2.1, October 2025. Eight sovereignty objectives, assessed on the levels SEAL 0 to SEAL 4. Cloud Sovereignty Framework (PDF) - BSI, Criteria enabling Cloud Computing Autonomy (C3A)official
Version 1.0 of April 27, 2026. Sovereignty criteria for cloud services, based on the objectives of the EU framework, without levels of their own. C3A (PDF) - European Commission, Cloud and AI Development Actofficial
COM(2026) 502 final of June 3, 2026, procedure 2026/0138 (COD). Provides for four Union Assurance Levels. As of September 1, 2026, at the preparatory stage in the European Parliament. digital-strategy.ec.europa.eu - US CLOUD Act, 18 U.S. Code § 2713legal text
Obligation to disclose data in the possession, custody or control of a provider, regardless of the storage location. Introduced in 2018. law.cornell.edu - European Data Protection Board, Guidelines 02/2024 on Article 48 GDPRofficial
Final version of June 5, 2025. Covers data requests from third-country authorities and the case of requests made via a parent company. edpb.europa.eu - German Security Clearance Check Act (SÜG), Section 4 (2)legal text
Definition of the four classification levels, including VS-NUR FÜR DEN DIENSTGEBRAUCH. gesetze-im-internet.de - BSI, The State of IT Security in Germany 2025 and 2024official
Source for the target group situation, the certificate figures and the BSI cloud strategy. bsi.bund.de/lagebericht
Information on ISEC7 products comes from our own product documentation and is marked as such. Third-party figures are always given with year and source.
Contact
Prefer to talk directly?
ISEC7 GmbH, Schellerdamm 16, 21079 Hamburg
The five building blocks in detail
As of: September 1, 2026. This page is reviewed and updated every six months.